Author: admin

  • EDO CYBERSECURITY SUMMIT 2025

    EDO CYBERSECURITY SUMMIT 2025

    #SpeakerSpotlightSeries
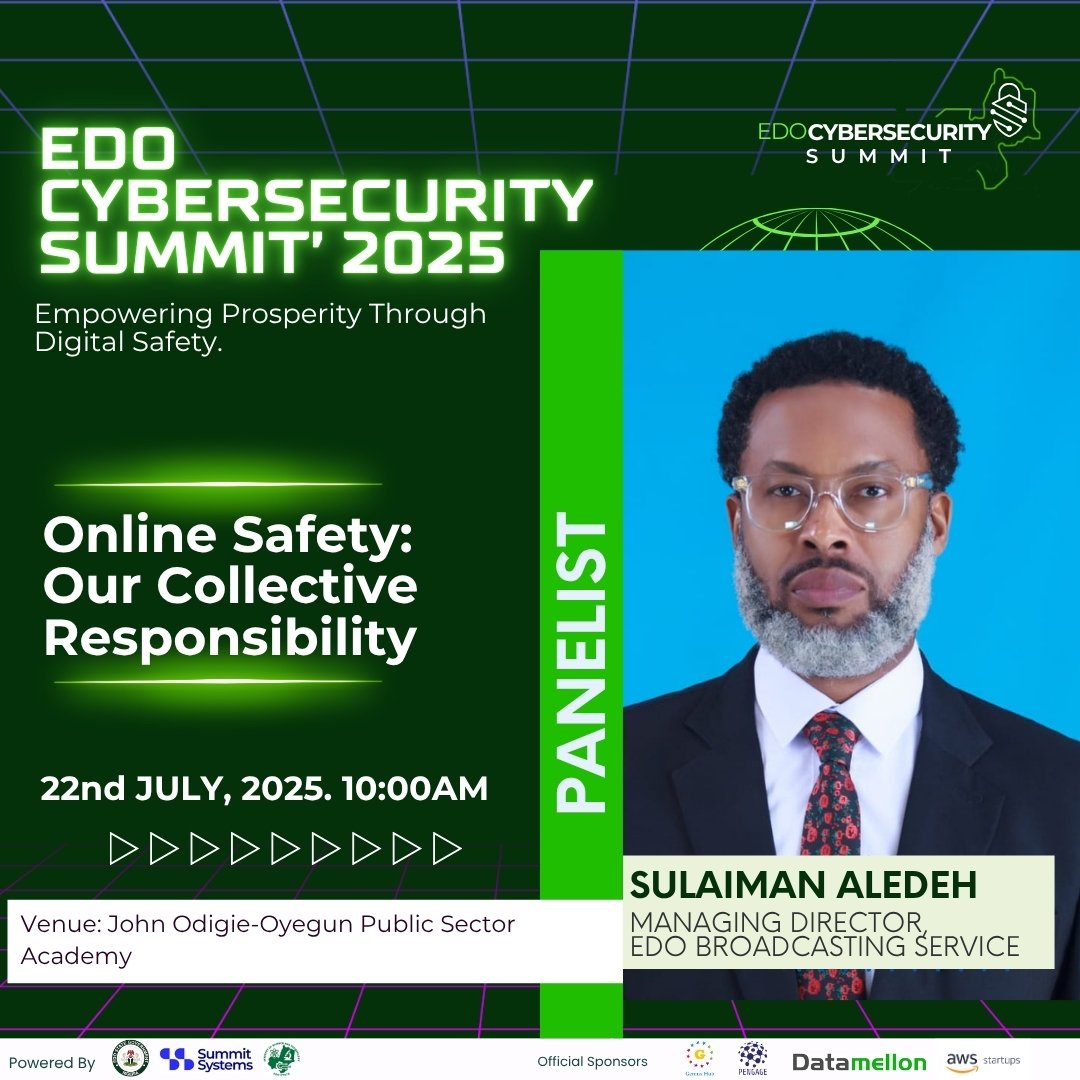
    We’re excited to feature Sulaiman Aledeh in this edition of our #SpeakerSpotlightSeries for the #EdoCybersecuritySummit2025!
    Stay tuned to learn more about his role, insights, and what to expect from his session at the summit!

    Sulaiman Aledeh is a distinguished International Journalist, Editor-at-Large, and Strategic Media and Communications Consultant, currently serving as the Managing Director and Editor-in-Chief at Edo Broadcasting Service. An alumnus of the prestigious U.S. State Department International Visitors Leadership Programme (Religious Freedom & Dialogue), he brings a wealth of experience and insight to his leadership role.

    With a rich career spanning over two decades, Sulaiman has made significant contributions to prominent international news outlets, including Al Jazeera, SABC, and GB News UK. Before his current appointment, he was a leading news anchor at Arise News, where he developed a reputation for delivering compelling and insightful coverage.

    In his previous role as Assistant General Manager and Head of Media and Communications at Eko Disco, Nigeria’s foremost electricity distribution company, Sulaiman honed his skills in strategic communication and public relations. His professional credentials include being a Fellow of the Institute of Public Diplomacy and Management and an Associate of the Nigeria Institute of Public Relations. He is also the founder of Aledeh Media Network, which operates gatekeepersnews.com, an integrated online media platform dedicated to providing quality news and analysis.

    Beginning his career as a pioneer staff member at one of Africa’s leading media corporations, Sulaiman has anchored flagship news programmes on News Central TV and TVC in Nigeria. His contribution to TVC’s grassroots governance programme, which aired on Radio and Television Continental, is particularly noteworthy.

    During his extensive tenure at Channels Television, he worked on political programmes that covered the 2011 and 2015 general elections. Sulaiman’s resourcefulness and resilience were crucial in leading teams that delivered over ten hours of continuous broadcasting during live election result coverage. His expertise was further highlighted during a special edition of Politics Today, which focused on the U.S. Presidential election.

    Academic excellence is a hallmark of Sulaiman’s profile; he holds a Master’s Degree in Humanitarian and Refugee Studies from the University of Lagos. Additionally, he has served as a Special Correspondent and News Anchor for Arise News in both London and Lagos.

    Sulaiman is well-known for creating the television programme Political Stew on TVC, which provided a comprehensive roadmap for the 2019 Nigerian General Elections. He replicated this success on News Central Television with the creation, anchoring, and production of Politics HQ, which served as a guide for Nigeria’s 2023 General Election.

    Beyond his impressive broadcasting career, Sulaiman is a certified voice expert in the Hudson Voice Technique, having been trained at Voice Master International in the UK. He has lent his voice to numerous major brands, including MTN, Glo, and DSTV. As a seasoned compere and anchor, he has hosted high-profile events such as the WimBiz Annual Conference in 2018, the unveiling of Governor Sanwo-Olu’s “Five Pillars of Development for Lagos,” and the Edo State Governorship debate.

    Sulaiman Aledeh’s diverse expertise, commitment to quality journalism, and leadership capabilities position him as a transformative force in the broadcasting landscape of Edo State and beyond.

    Want to hear Sulaiman Aledeh’s perspective on Online Safety: Our Collective Responsibility?

    Join us on July 22nd at the Edo Cybersecurity Summit 2025 in Benin City!

    🔗 Register now: https://lnkd.in/dwFQksDk
  • EDO CYBERSECURITY SUMMIT 2025

    EDO CYBERSECURITY SUMMIT 2025

    #SpeakerSpotlightSeries

    We’re excited to kick off our weekly #SpeakerSpotlightSeries for the #EdoCybersecuritySummit2025!

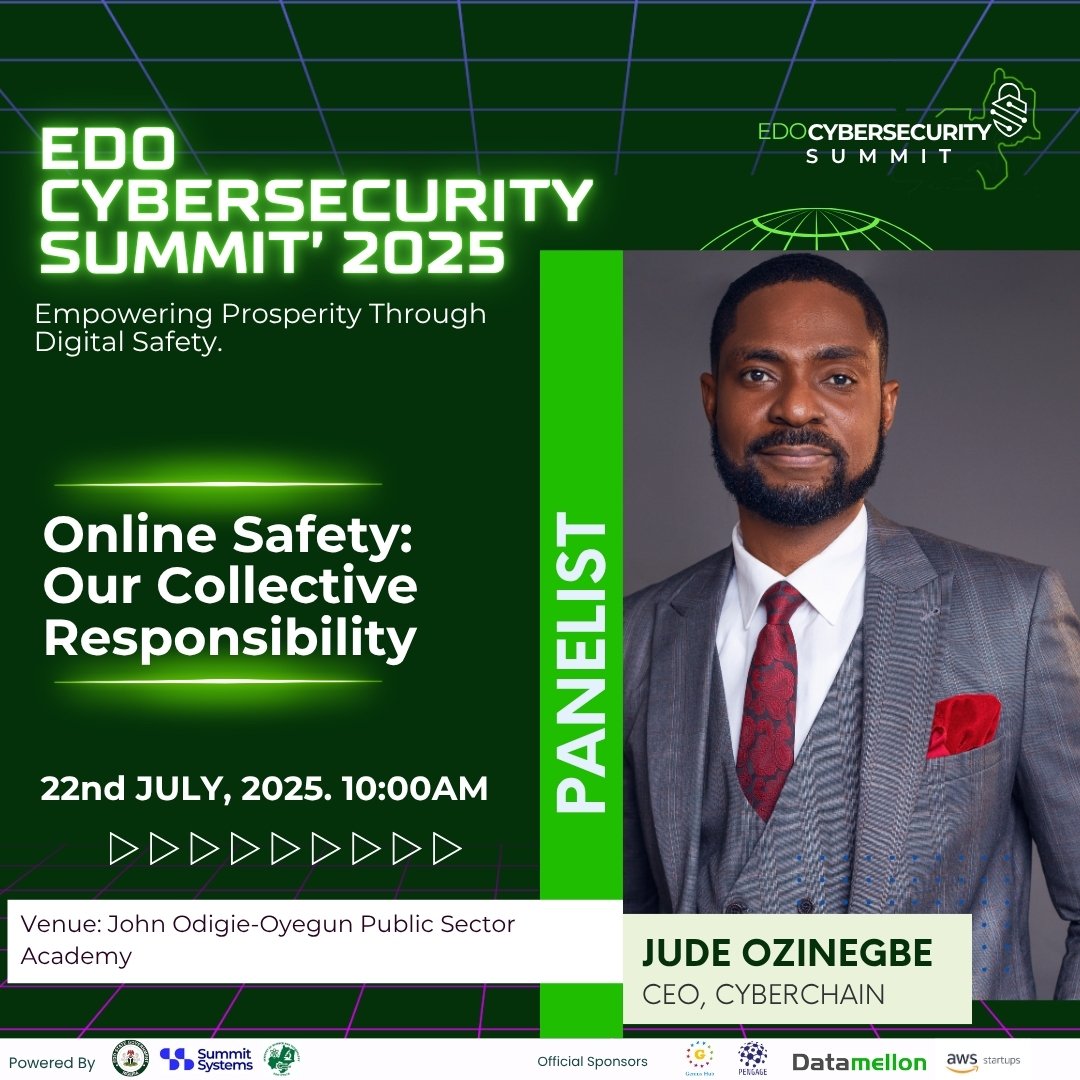
    Meet Jude Ozinegbe FIMC, CMC
    An accomplished Digital Security Expert and CEO of Cyberchain, who will be joining us as a Panelist at the Edo Cybersecurity Summit 2025!
    With over 20 years of experience in cybersecurity, blockchain, and tech education, Jude has led high-impact digital transformation projects, trained thousands—including executives from top institutions—and continues to champion digital trust and innovation across Africa.

    Jude Ozinegbe is a highly regarded Digital Security Expert with a proven track record in safeguarding digital assets, securing complex infrastructures, and promoting cyber resilience across industries. Jude is a computer Science graduate, with professional certifications from global technology leaders including Cisco, IBM, Fortinet, Google, and Microsoft, a Fellow of the Institute of Management Consultants and a Masters in Blockchain and Digital Currencies, Jude brings a multi-vendor, cross-platform approach to cybersecurity and digital infrastructure management.

    With over two decades of experience in the tech ecosystem, he has led and advised on numerous security transformation projects, enabling organizations to stay ahead of evolving cyber threats. His expertise spans network security, cloud security, identity and access management, incident response, threat intelligence, and compliance.

    His ICT Company, Zinochrome, has been instrumental to the success of numerous infrastructure projects in Nigeria.

    Passionate about digital trust and responsible innovation, Jude also engages in thought leadership, capacity building, and advocacy for secure digital transformation across Africa. He is a regular speaker at technology conferences and an active contributor to cybersecurity education and awareness initiatives.

    His contributions to the Tech education space in Nigeria has seen him train over 300 fellows on Cybersecurity under the 3MTT program – Abuja Cohort, with the Federal Ministry of Communications Innovation and Digital Economy in collaboration with NITDA and Domineum as well as over 900 fellows on Blockchain Technology at Baze University, Abuja also in partnership with the World Bank, NITDA and Domineum.

    Jude’s emerging technology focused company – Cyberchain has enabled him to work with startups, governments, and global enterprises, combining technical depth with strategic insights to deliver solutions that are secure, scalable, and future-ready.

    Jude has trained top executives from the Central Bank of Nigeria, Bayer Middle Africa, NITDA, ICP Blockchain, RedswanUSA, NLNG – Rwanda and many more too numerous to mention.

    Jude Ozinegbe is a powerhouse of human capacity development, yet a humble minister of the gospel.

    Want to hear Jude’s perspective on Online Safety: Our Collective Responsibility?
    Join us on July 22nd at the Edo Cybersecurity Summit 2025 in Benin City!
    🔗 Register now: https://lnkd.in/dwFQksDk
  • Regulatory Fire: NIBSS Fault & Flutterwave’s ₦21B Glitch — A Wake-Up Call for Nigeria’s Fintech Space and a Call for Cybersecurity Reform

    Regulatory Fire: NIBSS Fault & Flutterwave’s ₦21B Glitch — A Wake-Up Call for Nigeria’s Fintech Space and a Call for Cybersecurity Reform

    In a rapidly digitizing financial ecosystem, trust and reliability are the lifelines that power fintech innovation. However, recent events have shaken confidence in Nigeria’s digital payment infrastructure. A staggering ₦21 billion ($14 million) “glitch” involving Flutterwave — Nigeria’s leading fintech unicorn — and the Nigeria Inter-Bank Settlement System PLC (NIBSS) has triggered serious regulatory concerns and public debate.

    What Happened?

    In early 2025, Flutterwave reported an alarming incident: unauthorized transactions totaling over ₦21 billion were processed due to a “technical fault.” At the heart of this fault lies NIBSS, the centralized platform responsible for processing interbank payments and ensuring transaction integrity across Nigeria’s financial system.

    Investigations suggest that the glitch originated from a vulnerability in the NIBSS infrastructure that allowed multiple fraudulent or duplicate transactions to be processed without being flagged or halted. This breakdown in control mechanisms enabled bad actors to exploit the payment pipeline, leading to massive fund losses across several Flutterwave-linked accounts.

    The Fallout

    As soon as the incident came to light, the Central Bank of Nigeria (CBN) launched an inquiry into the integrity of the systems operated by both NIBSS and Flutterwave. This was more than just a cybersecurity oversight — it raised existential questions about the reliability of Nigeria’s financial rails.

    Flutterwave responded by initiating legal action and working with law enforcement agencies to freeze hundreds of accounts where the stolen funds were funneled. While a large portion of the money has been recovered or traced, the glitch underscores deeper systemic risks in the nation’s payment infrastructure.

    NIBSS, often viewed as the digital backbone of Nigeria’s banking sector, has maintained a measured silence, issuing a brief statement indicating an “internal review” was underway. However, industry insiders suggest that a major overhaul of NIBSS’ transaction monitoring systems may be inevitable.

    Implications for the Fintech Industry

    This isn’t just about one incident — it’s a warning shot for the broader Nigerian fintech ecosystem.

    1. Trust Deficit

    Consumers and partners are increasingly wary. If the country’s largest fintech and national settlement system can be breached or misfire at this scale, smaller players might be even more vulnerable.

    2. Increased Regulatory Scrutiny

    The Nigerian government, already cautious about the explosive growth of fintechs, may now impose stricter regulatory requirements — from mandatory third-party audits to real-time reporting systems. Compliance costs are expected to rise.

    3. Investor Anxiety

    Global investors, especially those eyeing Africa’s fintech boom, may adopt a wait-and-see approach. The episode may prompt due diligence teams to assess infrastructure risk more critically.

    4. Collaborative Security Models

    This crisis could spark more collaboration among fintechs, banks, and regulators to build a more resilient cybersecurity framework — potentially leading to a sector-wide cybersecurity council or NIBSS reform task force.

    The Bigger Picture

    This incident mirrors a global pattern: as digital payments increase, so does the scale and sophistication of systemic risks. Nigeria’s situation is unique in that NIBSS is a centralized hub — any fault there has a ripple effect across the entire banking and fintech landscape.

    The path forward will require transparency, technical accountability, and proactive regulation. For Flutterwave, this is a defining moment — not only to restore its reputation but to lead the charge for a safer, more secure fintech ecosystem in Africa.

    Conclusion

    The ₦21 billion glitch is more than a financial mishap — it’s a wake-up call. Nigeria’s digital financial infrastructure must evolve not just in innovation, but in integrity and resilience. When trust breaks in a payment ecosystem, so does confidence in the entire financial system.

    This is where cybersecurity must take center stage.

    Implementing robust cybersecurity frameworks — such as those aligned with international standards like NIST Cybersecurity Framework or ISO/IEC 27001 — can help fintechs and financial institutions anticipate, detect, and respond to threats more effectively. Real-time fraud detection systems, enhanced encryption, continuous vulnerability assessments, and secure software development lifecycles should become non-negotiable.

    Moreover, incident response plans must be tested regularly, with clear roles and rapid communication channels between banks, fintechs, and regulators like the CBN. Cybersecurity isn’t just an IT concern; it is now a strategic and regulatory imperative.

    As digital finance continues to expand across Africa, integrating cybersecurity into every layer of operation is no longer optional — it’s essential. A proactive, collaborative, and security-first approach is the only way forward to ensure trust, stability, and growth in Nigeria’s booming fintech landscape.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information

  • Trump Executive Order Rewrites U.S. Cybersecurity Playbook

    Trump Executive Order Rewrites U.S. Cybersecurity Playbook

    On June 6, 2025, President Donald Trump issued a sweeping Executive Order (EO) titled “Sustaining Select Efforts to Strengthen the Nation’s Cybersecurity.” It revises key aspects of both Biden-era EO 14144 (Jan 16, 2025) and Obama-era cybersecurity directives. The changes notably roll back digital identity initiatives and adjust how sanctions against cyber actors are applied.

    Narrowing Sanctions Authority

    • The EO restricts sanctions under existing cyber sanctions laws (e.g., EO 13694) to foreign malicious actors targeting critical infrastructure.
    • Sanctions will explicitly not apply in cases of election interference—even by foreign entities—unless they attack critical infrastructure
    • Critics warn the move potentially exempts foreign meddling in U.S. elections, raising accountability concerns

    Digital Identity Rollback

    • The EO scraps Biden’s digital identity provisions, which encouraged federal, state, and private sector deployment of remote identity verification (e.g., mobile driver’s licenses for accessing benefits)
    • According to the White House, this rollback aims to prevent the misuse of digital IDs for “entitlement fraud” by undocumented immigrants
    • Cybersecurity advocates caution that eliminating digital ID standards removes critical tools for reducing identity-related fraud and bolstering secure authentication frameworks

    Strengthening Core Cyber Tasks

    • The EO supports secure software development practices, mandating NIST, Commerce, and CISA to collaborate on standards for software integrity, timely patching, and supply chain security
    • It accelerates post-quantum encryption readiness, requiring the NSA and OMB to set encryption protocols resistant to future quantum threats by 2030
    • It directs agencies like DoD, DHS, ODNI, and NIST to develop frameworks to manage AI, IoT, and routing (BGP) vulnerabilities through stronger encryption and cross-agency coordination .

    What This Means

    1. Mixed Cybersecurity Signals
      While the EO strengthens some technical defenses (software hygiene, encryption, AI safeguards), the rollback of digital identity and narrowed sanctions may undermine long-term cyber resilience.
    2. Political vs. Technical Priorities
      The administration frames these rollbacks as removing “politically motivated” overreach—particularly around digital IDs and election-related sanctions—famously criticizing Biden’s EO as having “problematic and distracting issues”
    3. Implementation Concerns
      NIST, already affected by recent federal budget cuts, faces pressure to fulfill new mandates with fewer resources
      Meanwhile, ambiguous guidance on AI and IoT security may complicate adoption across federal agencies and the private sector.

    Expert Commentary

    • Mark Montgomery from the Foundation for Defense of Democracies warns: “The fixation on revoking digital ID mandates is prioritizing questionable immigration benefits over proven cybersecurity benefits”
    • Cybersecurity analysts note that while some reversals align with political rhetoric, they may weaken standardized approaches to identity verification and fraud prevention.

    Conclusion

    President Trump’s YOEO strikes a complex balance: enhancing technical safeguards like quantum-safe encryption and secure software, but also drawing back on digital identity programs and narrowing sanctions. This signals a pivot toward streamlined, infrastructure-focused cybersecurity, downplaying broader identity and election-related implications. Whether this approach will offer stronger resilience—or expose new vulnerabilities—depends heavily on agency follow-through, resource allocation, and potential Congressional response, especially concerning digital ID standards and election security.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information

  • Microsoft Teams Up with CBI to Bust Indian Call Center Scam Targeting Japan

    Microsoft Teams Up with CBI to Bust Indian Call Center Scam Targeting Japan

    In a major international cybersecurity crackdown, Microsoft has partnered with the Central Bureau of Investigation (CBI) to dismantle several illegal call centers in India that were behind a widespread tech support scam targeting Japanese citizens.

    The coordinated operation led to the raiding of multiple call centers across India, revealing a sophisticated scam network that impersonated Microsoft support representatives. The fraudsters would deceive unsuspecting Japanese users into believing their devices were compromised, then coerce them into paying for fake technical support services.

    According to Microsoft’s Cybercrime Investigation Team, this scam had been active for years and had defrauded thousands of Japanese victims. Victims were typically lured through fake pop-up alerts or misleading search engine ads, which directed them to call what they believed were official Microsoft helplines. Once on the line, operators would manipulate the victims using technical jargon and social engineering tactics to gain remote access to their computers and demand payments for unnecessary or non-existent repairs.

    Microsoft’s Digital Crimes Unit collaborated closely with CBI by providing intelligence, digital evidence, and technical support, which proved instrumental in tracing the scam to its origin. The company has been working globally to disrupt tech support fraud networks, having already assisted in dismantling similar operations in the United States, Europe, and other parts of Asia.

    “This successful operation underscores the importance of public-private partnerships in the fight against cybercrime,” said a Microsoft spokesperson. “We are committed to protecting users worldwide and holding cybercriminals accountable.”

    The CBI has confirmed the arrest of several suspects, seizure of digital equipment, and the freezing of bank accounts linked to the operation. Authorities are now working with Japanese law enforcement to assist affected victims and recover stolen funds.

    The case is a stark reminder of the growing global nature of cyber fraud, often spanning borders and exploiting trust in reputable brands like Microsoft. It also highlights the importance of cyber awareness and vigilance, especially among vulnerable users.

    Microsoft has urged users to remember:

    • Microsoft will never proactively reach out to offer unsolicited tech support.
    • Genuine Microsoft pop-ups will not request personal or financial information.
    • Users should report suspicious activity via the company’s support and fraud reporting portals.

    As investigations continue, both Microsoft and the CBI reaffirm their commitment to dismantling cybercrime syndicates and protecting digital citizens worldwide.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information

  • Victoria’s Secret Takes Website Offline Amid Serious Security Breach

    Victoria’s Secret Takes Website Offline Amid Serious Security Breach

    In a dramatic move that has caught the attention of the cybersecurity world and fashion retail industry alike, Victoria’s Secret has temporarily taken down its U.S. website following the discovery of a significant security incident. While the company has not revealed full details of the breach, it confirmed the precautionary shutdown is part of an active response to the issue. A statement posted on the brand’s homepage reads, “We are working around the clock to fully restore operations.”

    What We Know So Far

    On May 28, 2025, Victoria’s Secret initiated an emergency shutdown of its U.S. website and some in-store services. Customers looking to shop online have been greeted with a static message instead of the usual product pages and promotional banners.

    The company is currently working with third-party cybersecurity experts to investigate the nature and extent of the breach. As of now, no timeline has been provided for the full restoration of digital services.

    Customer Impact and Frustration

    The outage could not have come at a worse time—it overlapped with Memorial Day weekend, typically a major sales period for retailers. Users have taken to social media to express frustration over:

    Inability to place or track online orders

    Problems redeeming gift cards and promotional offers

    Concerns over delayed payroll access for employees

    In response, Victoria’s Secret has extended coupon expiry dates and return windows for affected customers. Physical store locations remain open, but some services like in-store returns for online purchases are temporarily suspended.

    Financial Fallout

    Digital sales make up over one-third of Victoria’s Secret’s $6.2 billion annual revenue. Following news of the incident, the company’s stock (NYSE: VSCO) dropped nearly 7%, signaling investor anxiety over the operational and reputational damage.

    Cybersecurity analysts speculate that this could be part of a broader pattern of attacks on major retailers, referencing recent breaches at Adidas, Marks & Spencer, and Co-op. Some experts warn that sophisticated cybercriminal groups like Scattered Spider could be involved, though no direct link has yet been confirmed.

    What Should Customers Do?

    Although the company hasn’t disclosed whether customer data has been compromised, experts recommend the following precautions:

    Monitor bank and card activity for unusual transactions.

    Change your Victoria’s Secret account password, especially if reused elsewhere.

    Be cautious of phishing emails or fake promotions pretending to be from the company.

    These steps can help protect your personal information while investigations continue.

    Key Takeaways for Businesses

    This incident serves as a major reminder: No company is too big to be targeted. Retailers handling large volumes of sensitive customer data must prioritize:

    Regular security audits

    Incident response planning

    Employee cybersecurity training

    Up-to-date data protection policies

    As threats evolve, so must defenses.

    Victoria’s Secret is in damage-control mode, and while customers are understandably upset, the company’s transparency and swift response will be critical in regaining trust.

    We’ll continue to monitor the situation and provide updates as more information becomes available. In the meantime, stay cyber-aware—and always use unique, strong passwords across your accounts.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information