Author: admin

  • Hackers Exploit Microsoft Entra ID to Access Sensitive Corporate Data

    Hackers Exploit Microsoft Entra ID to Access Sensitive Corporate Data

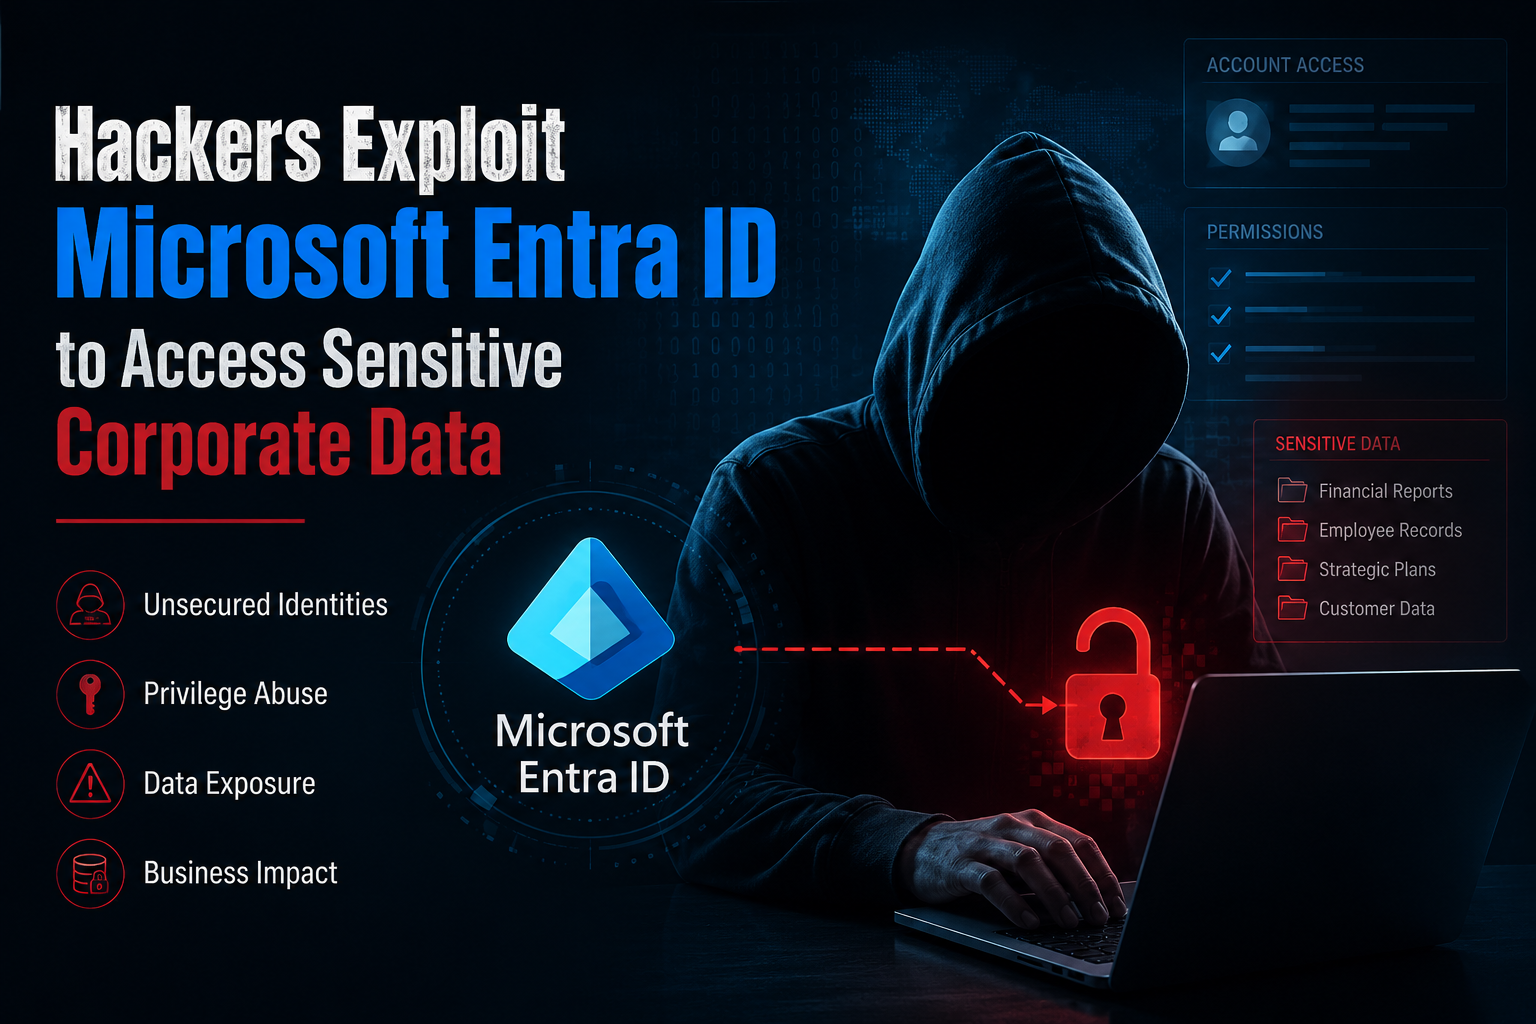
    Cybercriminals are increasingly targeting cloud identity platforms, and recent reports reveal a concerning trend: attackers are abusing compromised Microsoft Entra ID accounts to gain unauthorized access to sensitive data stored across Microsoft 365 and Microsoft Azure environments.

    Security researchers recently uncovered campaigns where threat actors leveraged tools such as TeamFiltration to target tens of thousands of Entra ID accounts globally. The attacks focused on account takeover, data exfiltration, and persistent access to enterprise cloud environments.

    For organizations relying heavily on Microsoft’s cloud ecosystem, this serves as another reminder that identity is now the primary security perimeter.

    Understanding the Attack

    According to cybersecurity reports, attackers used compromised credentials, API abuse, and legitimate Microsoft services to bypass traditional security controls. In many cases, threat actors did not rely on malware; instead, they abused trusted authentication mechanisms already present within organizations.

    The attack chain generally follows this pattern:

    1. Credential theft through phishing or social engineering
    2. Unauthorized login into Entra ID accounts
    3. Enumeration of Microsoft 365 and Azure resources
    4. Privilege escalation or persistence mechanisms
    5. Data exfiltration from cloud storage, email, and collaboration platforms

    Researchers noted that attackers leveraged legitimate APIs and cloud administration features, making detection significantly harder because activities often appeared as normal user behavior.

    Why Microsoft Entra ID Is a High-Value Target

    Microsoft Entra ID acts as the central authentication and identity management layer for many enterprises. Once attackers gain access to an Entra ID account, they may inherit access to:

    • Corporate emails
    • SharePoint and OneDrive data
    • Microsoft Teams conversations
    • Azure virtual machines and storage
    • Administrative dashboards
    • Third-party SaaS integrations

    Because Entra ID enables single sign-on (SSO), one compromised account can unlock multiple business-critical systems simultaneously.

    Key Risks to Organizations

    1. Silent Data Exfiltration

    Attackers can quietly export sensitive business information without deploying ransomware or triggering endpoint alerts.

    2. Persistence in Cloud Environments

    Threat actors may create additional identities, OAuth applications, or tokens to maintain long-term access.

    3. Abuse of Trusted Tools

    Using legitimate Microsoft APIs and administrative functions helps attackers evade conventional security monitoring.

    4. Business Disruption and Compliance Exposure

    Stolen customer data, intellectual property, or financial records can lead to operational downtime, reputational damage, and regulatory penalties.

    Indicators of Compromise

    Organizations should watch for:

    • Unusual login locations or impossible travel events
    • Suspicious OAuth application consent grants
    • Excessive Microsoft Graph API activity
    • Unexpected mailbox exports or SharePoint downloads
    • Privilege escalation attempts
    • Dormant accounts suddenly becoming active

    Continuous monitoring of identity activity is now essential for modern cybersecurity operations.

    How Organizations Can Protect Themselves

    Enable Multi-Factor Authentication Everywhere

    Strong MFA significantly reduces the effectiveness of credential theft attacks.

    Implement Conditional Access Policies

    Restrict access based on device trust, geography, user risk, and session behavior.

    Adopt Least Privilege Access

    Limit administrative privileges and regularly review access permissions.

    Monitor Identity and API Activity

    Deploy advanced identity threat detection and cloud security monitoring solutions.

    Review OAuth and Third-Party Integrations

    Attackers increasingly exploit excessive permissions granted to cloud applications.

    Conduct Regular Security Awareness Training

    Social engineering and phishing remain the most common entry points for attackers.

    The Bigger Cybersecurity Lesson

    Modern cyberattacks are shifting away from traditional malware toward identity-centric compromise. Attackers understand that cloud identities provide direct access to business operations, making them more valuable than endpoints alone.

    The abuse of Microsoft Entra ID accounts demonstrates how threat actors are evolving to exploit trust relationships within cloud ecosystems rather than relying solely on software vulnerabilities.

    Organizations must therefore move beyond perimeter-based security and adopt an identity-first security strategy that prioritizes:

    • Continuous authentication
    • Real-time monitoring
    • Zero Trust architecture
    • Cloud-native threat detection
    • Proactive incident response

    Final Thoughts

    The recent Entra ID abuse campaigns reinforce a critical reality: identity security is business security. As enterprises continue migrating workloads to the cloud, protecting identity platforms becomes essential to safeguarding data, operations, and customer trust.

    At Summit Systems ISSP, we encourage organizations to continuously assess their cloud security posture, strengthen identity protection mechanisms, and invest in proactive cybersecurity strategies that can detect and respond to modern threats before significant damage occurs.

    Cybercriminals are evolving rapidly — and organizations must evolve even faster.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information.
  • What the Canvas Cyber Incident Means for Universities and Why Cyber Resilience Matters

    What the Canvas Cyber Incident Means for Universities and Why Cyber Resilience Matters

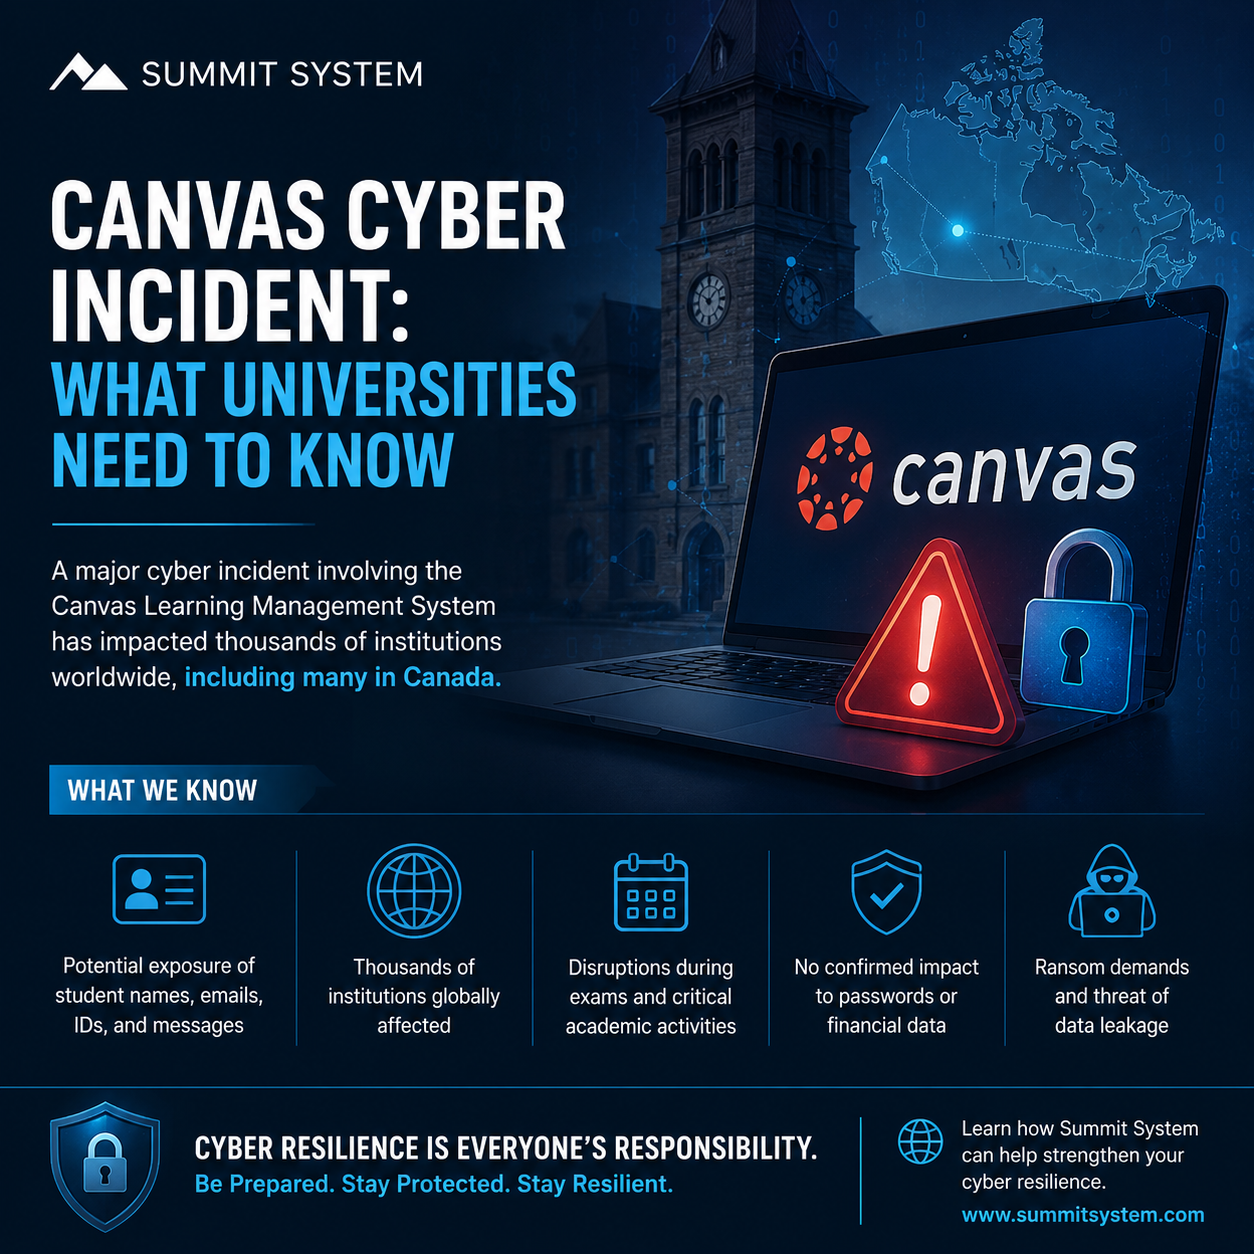
    The recent cyber incident involving the widely used Canvas Learning Management System (LMS) has become a wake-up call for universities and educational institutions around the world. Over the weekend, reports emerged that hackers targeted the platform used by thousands of schools and universities globally, disrupting online learning activities during one of the most critical periods of the academic calendar.

    For institutions that depend heavily on digital learning environments, the incident highlights an uncomfortable reality: education has become a prime target for cybercriminals.

    What Happened?

    Canvas, developed by Instructure, is one of the world’s most widely adopted learning management systems. The platform enables universities to manage coursework, assignments, exams, student communications, and online collaboration.

    According to public reports, threat actors allegedly gained unauthorized access to portions of the platform and disrupted services for multiple institutions. Some universities temporarily restricted access while investigations were underway.

    Early reports suggest that exposed information may include:

    • Student names
    • Email addresses
    • Student identification numbers
    • Internal messages and academic communications

    At the time of reporting, there has been no confirmed evidence that financial information or passwords were compromised. However, the event caused significant operational disruption during examination and coursework submission periods.

    Why Educational Institutions Are Increasingly Targeted

    Universities are particularly attractive to cybercriminals for several reasons:

    1. Large Volumes of Sensitive Data

    Educational institutions store:

    • Student records
    • Research data
    • Financial information
    • Staff credentials
    • Intellectual property

    This makes universities valuable targets for ransomware groups and data theft operations.

    2. Complex IT Environments

    Many institutions operate:

    • Legacy systems
    • Hybrid cloud environments
    • Third-party learning platforms
    • Open networks for students and faculty

    These interconnected systems can create security gaps if not continuously monitored and maintained.

    3. High Dependence on Availability

    When learning platforms go offline, academic operations can halt immediately. Cybercriminals understand the pressure institutions face during exams, admissions periods, and registration cycles.

    The Bigger Lesson: Cybersecurity Is Now Operational Risk Management

    The Canvas incident demonstrates that cybersecurity is no longer just an IT issue — it is an operational continuity issue.

    Organizations must prepare for:

    • Third-party vendor compromises
    • Supply chain attacks
    • Credential theft
    • Ransomware attempts
    • Data exfiltration incidents

    Even when an institution’s internal systems remain secure, vulnerabilities in external service providers can still create major disruption.

    Key Cybersecurity Measures Institutions Should Prioritize

    To strengthen resilience against similar incidents, organizations should consider:

    Vendor Risk Assessments

    Evaluate the cybersecurity posture of all third-party platforms and software providers.

    Multi-Factor Authentication (MFA)

    Reduce the risk of credential-based attacks by enforcing MFA across critical systems.

    Continuous Monitoring

    Implement real-time threat monitoring and incident detection capabilities.

    Incident Response Planning

    Develop and regularly test response plans for cyber incidents and service outages.

    Data Backups and Recovery

    Ensure secure backups are maintained and recovery procedures are validated.

    Security Awareness Training

    Educate staff and users on phishing, credential security, and suspicious activity reporting.

    Final Thoughts

    The Canvas cyber incident is another reminder that digital transformation must be matched with strong cybersecurity governance. As educational institutions continue to expand online learning and cloud-based collaboration, proactive cyber resilience becomes essential.

    At Summit Systems ISSP, we believe organizations must move beyond reactive security measures and adopt a comprehensive approach that combines prevention, detection, response, and recovery.

    Cyber threats are evolving rapidly — and resilience is now a critical business requirement, not an optional investment.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information

  • AI Biometric Scam Warning: Fact, Fiction, and What You Really Need to Know

    AI Biometric Scam Warning: Fact, Fiction, and What You Really Need to Know

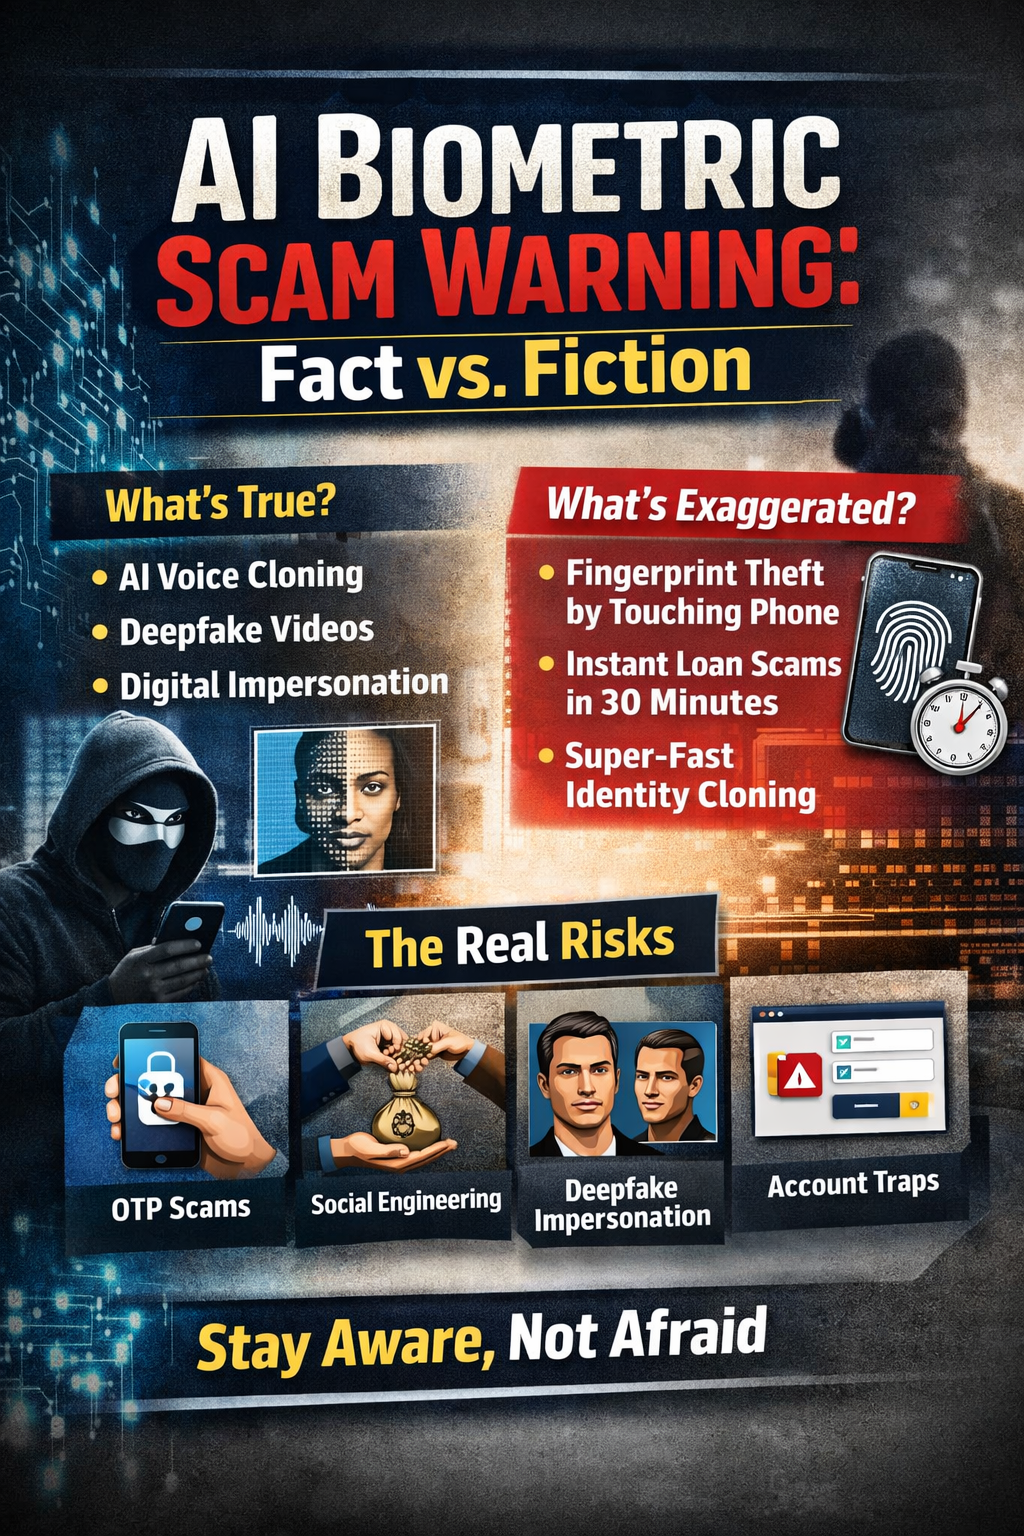
    Recently, a disturbing message has been circulating across WhatsApp and other social media platforms. The message warns of well-dressed strangers approaching people in public places — malls, markets, and transport stations — asking for help operating their phone. According to the claim, the phone is secretly recording video, capturing your fingerprint, voice, and facial data. Within 30 minutes, scammers allegedly use artificial intelligence (AI) to clone your identity and take out loans in your name.

    The message ends with urgent warnings: never help strangers with their phones, never read numbers aloud, and share the message to save others.

    It sounds alarming. But how much of it is actually true?

    Let’s examine the facts carefully.

    Understanding the Viral Claim

    The viral warning frames this as a new kind of “AI biometric identity scam.” It claims scammers are no longer interested in stealing your money directly — instead, they want your biometric data. According to the message, simply touching a stranger’s phone can capture your fingerprint, and speaking while looking at the screen allows AI to clone your voice and face.

    The scenario suggests that within minutes, scammers can create a digital version of you and use it to access financial services, apply for loans, and leave you with debt.

    The emotional tone is urgent and fear-driven, designed to make readers react quickly.

    But cybersecurity must be based on facts, not fear.

    What Is True: AI Voice and Face Cloning Exist

    Artificial intelligence has advanced significantly in recent years. Today’s AI tools can:

    • Clone a person’s voice using short audio samples
    • Generate realistic face videos known as deepfakes
    • Mimic facial expressions and speech patterns

    These technologies are real and are already being used in entertainment, research, and unfortunately, sometimes in scams.

    Digital impersonation is a genuine cybersecurity concern.

    However, having the technology and successfully using it to commit financial fraud instantly are two very different things.

    What Is Misleading: Fingerprint Theft by Touching a Phone

    One of the most alarming claims in the viral message is that touching a stranger’s phone allows scammers to capture your fingerprint.

    In reality, modern smartphones do not work this way.

    Fingerprint authentication systems:

    • Store encrypted fingerprint templates locally on the device
    • Do not store or expose actual fingerprint images to apps
    • Do not transmit fingerprint data through video calls or recordings

    Simply touching someone’s phone cannot transfer your fingerprint into their system.

    This part of the message is highly misleading and not supported by how biometric security works.

    Can Scammers Clone You and Take Loans in 30 Minutes?

    This is another major exaggeration.

    Financial institutions typically use multiple layers of security, including:

    • BVN (Bank Verification Number) or NIN verification in Nigeria
    • One-Time Passwords (OTP) sent to your registered phone number
    • Device authentication
    • Linked bank account verification
    • Multi-factor authentication

    Even with advanced AI, face or voice data alone is usually not enough to open accounts, approve loans, or transfer funds.

    Identity theft is possible, but it typically requires more information and access — not just a brief interaction in a public place.

    Real Risks That Actually Exist

    While the viral story exaggerates the threat, some real risks do exist in public and online interactions.

    These include:

    OTP scams: If you read a verification code sent to your phone aloud, scammers can use it to access your accounts.

    Social engineering: Scammers manipulate people using urgency, trust, or emotional pressure.

    Account login traps: Being tricked into entering your credentials on someone else’s device.

    Deepfake impersonation: Using publicly available videos and audio from social media to mimic individuals.

    These threats are real — but they typically require more direct cooperation or information from the victim.

    Why Fear-Based Messages Spread Quickly

    Messages like this often go viral because they use powerful psychological triggers, including:

    • Urgency (“30 minutes can ruin your life”)
    • Fear (“They don’t want your money. They want your identity.”)
    • Authority tone
    • Instructions to forward immediately

    Fear spreads faster than facts, especially when new technologies like AI are involved.

    People are more likely to share warnings that feel urgent, even if they are exaggerated.

    Practical Safety Tips Without Panic

    Instead of reacting with fear, focus on simple, effective digital safety practices:

    • Never share your OTP codes with anyone
    • Avoid logging into personal accounts on unfamiliar devices
    • Be cautious when handling strangers’ phones
    • Disconnect suspicious or unexpected video calls
    • Limit sharing sensitive personal content publicly
    • Enable multi-factor authentication on important accounts

    These basic precautions significantly reduce your risk.

    You do not need paranoia — you need awareness.

    Final Verdict: Real Technology, Exaggerated Scenario

    The viral “AI biometric cloning in 30 minutes” warning contains a mix of truth and exaggeration.

    AI voice and face cloning technologies are real.

    But the claim that scammers can instantly steal your fingerprint and drain your finances within minutes simply by handing you a phone is highly unlikely.

    The real threat is not magical AI identity theft in public spaces.

    The real threat is social engineering — scammers manipulating trust, urgency, and human behavior.

    Closing Thoughts

    Artificial intelligence is powerful, and its misuse is a legitimate concern. But misinformation and fear-based warnings can be just as harmful, causing panic and confusion.

    Before sharing alarming messages, take a moment to verify the facts.

    Cybersecurity is strongest when guided by knowledge, awareness, and calm decision-making — not fear.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information

  • Nike Investigates Alleged Cybersecurity Breach Following Data Leak Threats

    Nike Investigates Alleged Cybersecurity Breach Following Data Leak Threats

    Nike, one of the world’s most recognisable athletic brands, is currently investigating a potential cybersecurity incident after a notorious hacking group publicly claimed to have accessed its systems and threatened to release stolen data unless their demands are met.

    What Happened?

    On January 22, 2026, the WorldLeaks cybercrime gang added Nike to its darknet leak site — a platform frequently used by threat actors to list alleged victims and apply public pressure for ransom payments. The group has positioned a countdown timer, indicating that the purportedly stolen data will be published by January 24 unless negotiations occur. At the time of publishing, neither the volume nor the exact nature of the data allegedly compromised has been fully confirmed.

    Nike has issued a brief statement emphasizing its commitment to consumer privacy and data security, saying it is actively investigating the potential incident and assessing the situation.

    Who Are the Attackers?

    WorldLeaks emerged in 2025 following the dissolution of a previous ransomware syndicate known as Hunters International. Unlike traditional ransomware groups that encrypt systems and demand payment to restore access, WorldLeaks and similar outfits focus primarily on data theft and extortion — threatening to leak sensitive information unless their financial demands are met.

    Security analysts have tied WorldLeaks’ activity to broader trends in extortion-driven cybercrime, where data exfiltration and public disclosure threats have become increasingly common tactics.

    What Is at Stake?

    Details on what exactly was taken remain scarce. Cybersecurity reports suggest the leak could include internal documents, credential lists, and possibly customer or partner data — though these claims are unverified as of now. One independent report mentioned that thousands of internal records may be involved, but official confirmation from Nike remains pending.

    Threat actors like WorldLeaks often employ phishing, exploitation of exposed services, or stolen credentials to gain initial access to corporate networks, though specifics of this incident haven’t been disclosed.

    Broader Context: A Growing Trend

    This event comes amidst a spate of cybersecurity incidents affecting major brands and organisations across industries — from retail to technology and healthcare. In several recent cases, groups have either leaked or threatened to leak sensitive information after claiming access to corporate databases.

    For organisations like Nike, the implications extend beyond immediate operational risk. Public exposure of compromised data can erode customer trust, trigger regulatory scrutiny, and lead to costly remediation if personal information is involved.

    How Companies Can Respond

    In situations like this, best practices for organisations under threat include:

    • Immediate incident response activation, including forensic analysis of affected systems.
    • Transparent communication with stakeholders and affected parties without releasing sensitive internal details.
    • Engagement with experienced cybersecurity partners to guide containment and recovery.
    • Monitoring dark web channels for further threat actor activity related to the incident.

    Proactive measures such as multi-factor authentication (MFA), robust network segmentation, and regular employee security training can also reduce the likelihood of successful intrusions.

    Conclusion

    Nike’s ongoing investigation highlights the evolving tactics of cybercriminals and the tangible risks modern enterprises face in an increasingly digital business environment. While the full impact of the alleged breach remains unclear, the situation underscores the importance of robust cybersecurity posture, rapid incident response, and vigilant monitoring of emerging threats.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information

  • Two US rusted Cybersecurity Professionals Plead Guilty in Major Ransomware Extortion Case

    Two US rusted Cybersecurity Professionals Plead Guilty in Major Ransomware Extortion Case

    Two U.S.-based cybersecurity professionals have pleaded guilty in federal court for their roles in spearheading ransomware attacks that extorted multiple victims across the United States, according to the U.S. Department of Justice.

    The defendants, Ryan Clifford Goldberg of Georgia and Kevin Tyler Martin of Texas, both formerly employed in respected cybersecurity roles, admitted to conspiring to obstruct, delay, or affect commerce through extortion by deploying the notorious ALPHV/BlackCat ransomware in 2023.

    Background & Scope of the Case

    Goldberg and Martin — who previously worked as an incident response manager and a ransomware negotiator, respectively — used their professional expertise and trusted access to identify, infiltrate, and compromise corporate networks.

    The pair operated as affiliates of the BlackCat ransomware group, paying a portion of ransom proceeds to the malware’s administrators in exchange for access to the ransomware platform.

    According to court records, the defendants and a third unnamed co-conspirator targeted numerous U.S. companies, including victims in healthcare, engineering, and technology sectors. In one instance, a Florida medical company paid over $1.2 million in Bitcoin to regain access to encrypted files — funds that were subsequently laundered.

    Consequences & Legal Outcomes

    Goldberg and Martin have entered guilty pleas to federal charges of conspiracy to commit extortion. They face up to 20 years in prison, and sentencing has been scheduled for March 12, 2026.

    In addition to potential incarceration, both defendants are expected to forfeit proceeds derived from the illicit scheme as part of their plea agreements.

    Industry Impact & Lessons Learned

    This case marks a sobering reminder that insider threats — even from experienced cybersecurity professionals — pose real and evolving risks to organizations. It underscores several key imperatives for businesses and security teams:

    • Vetting & Oversight: Robust background screening and continuous monitoring of personnel with privileged system access is essential.
    • Ethics & Accountability: Strong ethical codes and enforceable professional standards in cybersecurity can deter misuse of skills for illicit ends.
    • Third-Party Risk Management: Organizations must evaluate not only their internal teams but also the trustworthiness of external partners, especially those engaged in incident response and threat mitigation services.

    Closing Thought

    While ransomware remains a pervasive global threat, cases like this highlight the deep importance of integrity in the cybersecurity profession. Upholding trustworthiness and ethical conduct isn’t just best practice — it’s foundational to protecting businesses, clients, and digital infrastructure.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information

  • Happy New Year from all of us at Summit Systems ISSP!

    As we step into this new year, we want to sincerely appreciate everyone who has been part of our journey and success.

    To our partners and collaborators, thank you for your trust, strong partnerships, and continued support. Together, we are building resilient systems and shaping a more secure digital future.

    To our team members and colleagues, your dedication, professionalism, and passion remain the driving force behind our vision. Your commitment to excellence does not go unnoticed.

    To our trainees, interns, and learners, thank you for choosing Summit Systems ISSP. Your curiosity, discipline, and eagerness to grow in cybersecurity inspire us daily. We are proud to be part of your professional journey.

    To our facilitators, mentors, instructors, and reviewers, thank you for generously sharing your knowledge, guidance, and expertise. Your impact continues to shape the next generation of cybersecurity professionals.

    To our supporters, clients, community members, and well-wishers, we appreciate your encouragement and belief in our mission.

    As we embrace the year ahead, we look forward to stronger collaborations, greater impact, innovation, and shared success.

    Here’s to a year of growth, excellence, and new opportunities for us all.

    #HappyNewYear #SummitSystemsISSP #Cybersecurity #Gratitude #Growth #Collaboration #Excellence