Author: admin

  • Critical OpenSSH Vulnerabilities Expose Systems to Man-in-the-Middle and DoS Attacks — Patch Immediately!

    Critical OpenSSH Vulnerabilities Expose Systems to Man-in-the-Middle and DoS Attacks — Patch Immediately!

    Critical OpenSSH Vulnerabilities Discovered

    Security researchers have recently disclosed multiple vulnerabilities in OpenSSH, the widely used open-source implementation of the SSH protocol. These flaws could allow attackers to launch Man-in-the-Middle (MitM) attacks and Denial-of-Service (DoS) attacks, putting countless systems at risk. Organizations relying on OpenSSH for secure remote access should immediately patch their systems to mitigate these threats.

    Overview of the Vulnerabilities

    The newly identified vulnerabilities affect OpenSSH versions prior to the latest security patch. The two most critical flaws include:

    1. Man-in-the-Middle Attack Vulnerability(CVE-2024-####)
      • Attackers can intercept SSH traffic, potentially decrypting session data or injecting malicious commands.
      • This flaw stems from improper validation of SSH handshake integrity, allowing adversaries to manipulate authentication processes.
    2. Denial-of-Service (DoS) Vulnerability(CVE-2024-####)
      • Malicious actors can send specially crafted SSH messages, causing excessive CPU and memory consumption.
      • This can lead to system crashes or service disruptions, affecting business operations.

    Potential Impact on Organizations

    If exploited, these vulnerabilities could have severe consequences:

    • Compromised Authentication: Attackers can intercept or alter authentication requests, leading to unauthorized access.
    • Data Theft & Manipulation: Sensitive data transmitted over SSH sessions could be exposed.
    • Service Disruptions: Critical services relying on SSH for secure communications could be rendered inoperable.

    Mitigation & Recommended Actions

    Summit Systems ISSP strongly advises organizations to take the following actions immediately:

    1. Patch OpenSSH Immediately
      • Upgrade to the latest OpenSSH version that addresses these vulnerabilities.
      • Check official OpenSSH repositories and security advisories for the latest patch details.
    2. Enable Strict SSH Configurations
      • Use strict key exchange algorithms and disable outdated cryptographic protocols.
      • Implement multi-factor authentication (MFA) to enhance access security.
    3. Monitor & Audit SSH Traffic
      • Regularly review SSH logs for unusual login attempts or anomalies.
      • Deploy intrusion detection systems (IDS) to identify suspicious SSH activity.
    4. Restrict SSH Access
      • Limit SSH access to only necessary users and IP ranges.
      • Implement firewall rules to prevent unauthorized SSH connections.

    Conclusion

    With the growing threat landscape, ensuring the security of OpenSSH implementations is critical. Organizations should act immediately by applying patches, strengthening security configurations, and monitoring SSH activity. Summit Systems ISSP remains committed to helping businesses stay ahead of cyber threats through proactive security strategies.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information.
  • Global Crackdown on Cybercrime: US, UK, and Australia Target Russia-Based Zservers for Alleged Ties to LockBit Ransomware

    Global Crackdown on Cybercrime: US, UK, and Australia Target Russia-Based Zservers for Alleged Ties to LockBit Ransomware

    In a coordinated effort to disrupt cybercriminal operations, the United States, United Kingdom, and Australia have taken decisive actions against Russia-based Zservers, a hosting provider allegedly linked to the notorious LockBit ransomware group. These measures are part of a broader international crackdown on cyber threats that have targeted critical infrastructure, businesses, and government agencies worldwide.

    LockBit Ransomware: A Persistent Cyber Threat

    LockBit ransomware has been one of the most prolific cyber threats in recent years, responsible for numerous high-profile attacks across multiple sectors. The group employs a ransomware-as-a-service (RaaS) model, allowing affiliates to use its malware to conduct attacks in exchange for a share of the ransom payments. Its sophisticated encryption techniques, stealthy operations, and double extortion tactics—where attackers not only encrypt files but also threaten to leak sensitive data—have made it a formidable force in the cybercrime landscape.

    Zservers’ Alleged Role in LockBit Operations

    Authorities from the US, UK, and Australia have identified Zservers, a Russia-based hosting provider, as a key facilitator of LockBit’s infrastructure. According to cybersecurity experts, Zservers has provided bulletproof hosting services, enabling ransomware operators to evade law enforcement and maintain resilient attack operations. Bulletproof hosting providers offer a high degree of anonymity and protection from takedowns, making them attractive to cybercriminal groups.

    In response, law enforcement agencies have imposed sanctions, seized servers, and restricted financial transactions linked to Zservers. These actions aim to disrupt the operational backbone of LockBit and hinder its ability to launch future attacks.

    International Collaboration in Cybersecurity Enforcement

    The move against Zservers highlights the growing importance of international collaboration in cybersecurity enforcement. The US Department of Justice (DOJ), the UK’s National Crime Agency (NCA), and the Australian Cyber Security Centre (ACSC) have been working together to track and dismantle LockBit’s infrastructure.

    These coordinated efforts build upon previous crackdowns, such as the takedown of ransomware networks and the arrest of key cybercriminals involved in ransomware operations. The sanctions and asset freezes imposed on Zservers and associated entities serve as a warning to other cybercriminal facilitators who enable malicious activities.

    Impact on Ransomware Ecosystem

    While this action marks a significant victory against ransomware groups, experts warn that cybercriminals are highly adaptive. With their infrastructure disrupted, LockBit operators may seek alternative hosting services or employ decentralized techniques to evade future enforcement actions. However, the increased scrutiny on hosting providers and financial networks supporting ransomware groups is expected to create more obstacles for cybercriminal operations.

    Moreover, businesses and organizations are urged to strengthen their cybersecurity postures by implementing robust defenses, conducting regular security audits, and fostering resilience against ransomware threats. Governments continue to advocate for cybersecurity awareness, encouraging companies to adopt best practices such as network segmentation, multi-factor authentication, and zero-trust security models.

    Conclusion

    The targeting of Russia-based Zservers by the US, UK, and Australia underscores the international commitment to combating ransomware threats. As cybercriminal groups evolve, so too must the strategies used to counter them. With enhanced cooperation, stronger cybersecurity policies, and proactive enforcement actions, the global fight against ransomware continues to gain momentum.

    Organizations must remain vigilant, adopt comprehensive security measures, and collaborate with cybersecurity experts to mitigate risks posed by evolving cyber threats. The crackdown on Zservers serves as a reminder that no cybercriminal infrastructure is beyond the reach of international law enforcement.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information.
  • Cyber Threat Alert: Fraudulent Google Play and Amazon Gift Card Phishing Schemes.

    Cyber Threat Alert: Fraudulent Google Play and Amazon Gift Card Phishing Schemes.

    Introduction

    Cybercriminals are deploying sophisticated phishing campaigns using hundreds of malicious domains to trick users into revealing their personal information. These scams falsely promise free Google Play and Amazon gift cards, luring victims into entering sensitive details such as email addresses, passwords, and financial data. Understanding how these scams work and recognizing warning signs is crucial in protecting yourself and your organization from cyber threats.

    How the Scam Works

    Fake Websites – Attackers create fraudulent websites that closely resemble legitimate reward sites, making it difficult for users to distinguish between real and fake offers.

    Social Engineering – Victims are enticed with attractive offers of free gift cards or promotional rewards.

    Data Harvesting – Once a user engages, they are prompted to enter sensitive information, including login credentials and payment details.

    Malware Distribution – Some of these sites also distribute malware, which can steal credentials, monitor user activity, or exploit system vulnerabilities.

    Indicators of a Scam

    Recognizing the red flags of phishing scams can help prevent falling victim to these malicious tactics:

    Too Good to Be True Offers – If an offer seems unrealistically generous, it likely is a scam. Legitimate companies rarely give away free gift cards without conditions.

    Suspicious URLs – Check website addresses carefully for misspellings, extra characters, or unknown domains.

    Requests for Personal Information – Be cautious if a site asks for login credentials, passwords, or credit card details in exchange for a reward.

    Urgency and Pressure Tactics – Scammers often create a sense of urgency, claiming that an offer is limited and pushing users to act fast.

    How to Stay Safe: Protect yourself and your organization by following these cybersecurity best practices:

    ✔ Verify the Source – Always confirm the legitimacy of any promotion by visiting the official website or contacting customer support.

    ✔ Use Multi-Factor Authentication (MFA) – Enabling MFA adds an extra layer of security to prevent unauthorized access to your accounts.

    ✔ Check Website Security – Ensure the site uses HTTPS and comes from a trusted domain before entering any personal details.

    ✔ Report Suspicious Sites – If you encounter a fraudulent website, report it using platforms like Google Safe Browsing to help protect others.

    Conclusion

    As cybercriminals continue to evolve their tactics, awareness and vigilance remain the best defense against phishing scams. Organizations and individuals should stay informed, verify sources, and implement cybersecurity best practices to avoid falling victim to these fraudulent schemes. By recognizing scam indicators and adopting proactive security measures, you can safeguard your personal and financial information from cyber threats.

    For more cybersecurity insights and protection tips, stay connected with Summit Systems.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information.
  • Microsoft Addresses Critical Authentication Bypass Vulnerability (CVE-2025-21396)

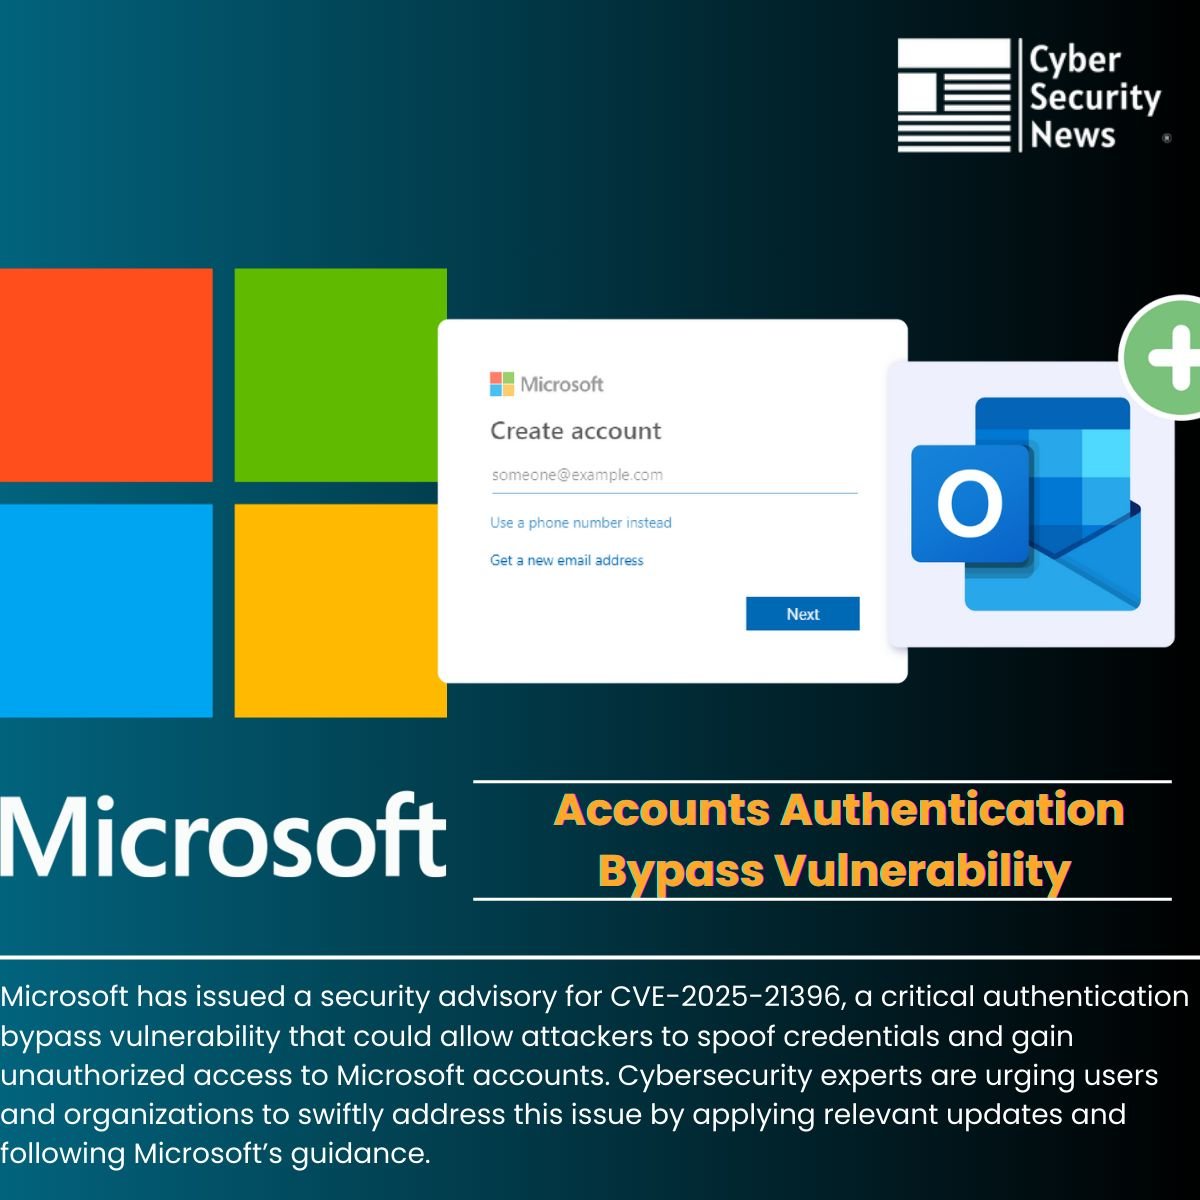
    Microsoft Addresses Critical Authentication Bypass Vulnerability (CVE-2025-21396)

    In a crucial security update, Microsoft has issued an advisory for CVE-2025-21396, a critical authentication bypass vulnerability that could enable attackers to spoof credentials and gain unauthorized access to Microsoft accounts. Summit Systems strongly advises organizations and individuals to take immediate steps to mitigate the associated risks.

    Understanding CVE-2025-21396

    CVE-2025-21396 is associated with CWE-290 (Authentication Bypass by Spoofing), a recognized security weakness affecting authentication mechanisms that lack robust validation methods. Malicious actors can exploit trust-based authentication models using techniques such as:

    • IP Spoofing: Attackers forge source IP addresses to impersonate trusted systems and gain unauthorized access.
    • DNS Spoofing: Manipulating DNS responses to redirect users to attacker-controlled domains.
    • Malformed or Manipulated Requests: Exploiting weak validation logic in application-layer protocols to bypass authentication measures.

    Due to the prevalent reliance on IP and DNS-based trust models, this vulnerability poses a significant risk, necessitating immediate remediation.

    Attack Scenarios and Potential Impact

    The vulnerability may be exploited in multiple ways, including:

    • Bypassing IP-Based Authentication: Organizations that rely solely on IP addresses for authentication may be at risk, as attackers can forge IP addresses to appear as trusted entities, bypassing security measures.
    • DNS-Based Host Verification Manipulation: Attackers can poison DNS caches, causing systems to trust a malicious domain masquerading as a legitimate Microsoft service.

    Considering the relative ease of executing IP spoofing and DNS cache poisoning attacks, CVE-2025-21396 is classified as a critical vulnerability with a high likelihood of exploitation.

    Microsoft’s Security Guidance & Recommended Mitigations

    Microsoft has issued patches to address CVE-2025-21396 and urges all users and organizations to apply security updates without delay. Summit Systems further recommends the following best practices:

    1. Apply Security Updates: Regularly update all systems and software by following Microsoft’s Security Update Guide.
    2. Strengthen Authentication Mechanisms:
      • Implement Multifactor Authentication (MFA) for enhanced security.
      • Utilize cryptographic tokens for secure identity validation.
      • Deploy Mutual TLS (mTLS) for encrypted and authenticated connections.
    3. Monitor Networks for Anomalies: Deploy Intrusion Detection Systems (IDS) to detect spoofed packets and unusual DNS activity.
    4. Harden DNS Infrastructure: Implement DNS Security Extensions (DNSSEC) to safeguard against DNS spoofing and maintain data integrity.
    5. Enable Logging & Auditing: Maintain comprehensive logs of authentication attempts to facilitate forensic analysis in the event of an attack.

    While Microsoft has addressed CVE-2025-21396 with the latest security updates, organizations must take proactive measures such as strengthening authentication frameworks and enhancing network monitoring to reduce exposure to similar threats in the future.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information.
  • Massive PowerSchool Data Breach Exposes Millions of Student and Educator Records

    Massive PowerSchool Data Breach Exposes Millions of Student and Educator Records

    The education sector is facing one of the most significant data breaches in recent history, as PowerSchool, a leading provider of Student Information Systems (SIS) in the U.S. and Canada, confirmed that hackers had stolen vast amounts of historical data from school districts. The breach, which has already impacted millions of students and educators, raises serious concerns about data security in educational institutions.

    On January 7, 2025, PowerSchool disclosed that attackers had accessed its SIS service through the PowerSource customer support portal. This breach enabled them to steal extensive personal data, including:

    • Names and contact information
    • Dates of birth
    • Medical records
    • Social Security numbers
    • Disability information
    • Race, ethnicity, and gender data
    • Parent/guardian/emergency contact details

    School districts confirmed that records dating back to 1985 were compromised, impacting over 72 million individuals, including 62.5 million students and 9.5 million educators across the U.S. and Canada.

    How Did This Happen?

    PowerSchool initially cited a “compromised credential” as the entry point for the breach. The Menlo Park City School District (MPCSD) reported that the compromised credential belonged to a maintenance account, granting broad access to customer data. Security researchers suspect that information-stealing malware may have been used to obtain this login information.

    The breach was detected on December 28, 2024, but evidence suggests that hackers had been exfiltrating data since December 22 using an export data manager. Despite working with cybersecurity firm CrowdStrike to investigate the breach, PowerSchool has not publicly disclosed further details about the attack.

    A Growing Crisis: Lawsuits and Fallout

    As more school districts reveal the extent of their data exposure, legal and reputational consequences for PowerSchool continue to mount:

    • Over 20 lawsuits have already been filed against the company.
    • School districts, including the Toronto District School Board (TDSB), reported that 1.5 million students were affected.
    • Data from 6,500 school districts may have been stolen, making this one of the largest education sector breaches to date.

    Despite claims that the stolen data was deleted after a ransom payment was made, PowerSchool is providing impacted individuals with two years of free identity theft and credit monitoring services.

    What Can Schools and Educators Do?

    Given the scale of this breach, affected institutions and individuals must take proactive steps to protect their data:

    1. Review Security Logs – Schools using PowerSchool’s SIS should analyze logs to determine the extent of data exfiltration.
    2. Monitor for Identity Theft – Impacted individuals should take advantage of PowerSchool’s credit monitoring offer and watch for suspicious activity.
    3. Strengthen Authentication Measures – Institutions should implement multi-factor authentication (MFA) and regularly rotate administrative credentials.
    4. Enhance Cybersecurity Training – Educators and administrators should be trained on recognizing phishing attempts and safeguarding sensitive information.

    Final Thoughts

    This breach highlights the urgent need for stronger cybersecurity measures in the education sector. Schools must reassess their security strategies to prevent future incidents, and vendors like PowerSchool must ensure that their systems are more resilient against cyber threats. Summit Systems is committed to helping organization bolster their cybersecurity defenses through advanced risk management strategies and compliance solutions.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information.
  • Beware of Scammers Exploiting the Los Angeles Wildfires: How to Stay Protected

    Beware of Scammers Exploiting the Los Angeles Wildfires: How to Stay Protected

    In the wake of the devastating Los Angeles wildfires, cybercriminals are exploiting the crisis to scam unsuspecting victims and good Samaritans. As individuals and organizations rally to provide relief and support, scammers are leveraging the panic and goodwill to steal money and sensitive information. A recent investigation by the cybersecurity company Before AI sheds light on these fraudulent tactics and provides valuable insights into how to stay safe.

    Fraudulent Domains Targeting Victims

    Between January 8th and January 13th, 2025, BforeAI identified 119 suspicious domains registered at the height of the wildfire crisis. These domains were strategically designed with keywords such as “LA fire,” “wildfire,” “relief,” “fund,” and “rebuild,” aiming to capitalize on trending topics in the media. Half of these domains were registered through GoDaddy, a web hosting service recently criticized by the Federal Trade Commission for inadequate cybersecurity measures. Other platforms involved include Namecheap, Register, Ionos, Hostinger, Squarespace, and Tucows.

    Scammers have also taken advantage of top-level domains (TLDs) to build credibility. Seventy percent of the fraudulent sites used the “.com” TLD, while others opted for “.fund,” subtly hinting at their malicious intent to steal donations from unsuspecting victims.

    Fake GoFundMe Campaigns

    A significant number of fake GoFundMe campaigns emerged during the wildfires. These campaigns often tugged at heartstrings by showcasing injured or lost pets purportedly affected by the fires. However, many of these images were stolen from other sources, including previous scam campaigns or unrelated legitimate fundraisers.

    One fake campaign, titled “Aid Our Recovery from LA Fire Tragedy,” claimed to support a dog injured by the wildfires. However, the photo used was traced to an unrelated fundraiser for a dog battling cancer.

    Scammers also posed as individuals and organizations offering shelter and care for displaced animals. Their fraudulent activities not only misdirected funds away from legitimate causes but also exploited the trust of well-meaning donors.

    Merchandise and Cryptocurrency Scams

    Beyond fake fundraisers, scammers launched merchandise stores falsely claiming to support wildfire victims. Some even impersonated the Los Angeles Fire Department, selling items supposedly tied to relief efforts.

    Additionally, new cryptocurrency schemes surfaced, promising quick financial gains while capitalizing on the wildfire’s media attention. These “pump and dump” schemes targeted victims who had already suffered financial losses, luring them with the promise of rapid returns. Social media platforms amplified these schemes, helping scammers reach broader audiences.

    How to Stay Protected

    To safeguard yourself and your donations during times of crisis, follow these guidelines:

    Verify Domains: Be cautious when visiting websites related to disaster relief. Look for official sites and verify their legitimacy before making any donations.

    Research Fundraisers: Always verify GoFundMe campaigns and other fundraisers. Look for credible information about the organizer and cross-check photos and stories.

    Avoid Impulse Donations: Take time to research organizations and campaigns. Donate directly to reputable and established charities.

    Be Skeptical of Merchandise Claims: Avoid buying merchandise claiming to support relief efforts unless you can verify the seller’s authenticity.

    Beware of Cryptocurrency Schemes: Avoid investing in new or unverified cryptocurrency projects, especially those tied to trending disasters.

    Report Suspicious Activity: If you come across a suspicious campaign or domain, report it to the appropriate authorities or cybersecurity organizations.

    Final Thoughts

    The Los Angeles wildfires have left countless individuals and families in need of support. While many are stepping up to help, cybercriminals are exploiting the situation for personal gain. By staying vigilant and informed, you can ensure your contributions make a genuine difference and protect yourself from falling victim to these malicious schemes.

    Summit Systems remains committed to raising awareness about cybersecurity threats and empowering individuals and organizations to navigate the digital landscape safely.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information