Tag: attackers

  • Chinese Hackers Shift Tactics: IT Supply Chains Now Under Attack

    Chinese Hackers Shift Tactics: IT Supply Chains Now Under Attack

    Cybersecurity threats have evolved dramatically, with state-sponsored actors increasingly targeting critical infrastructures worldwide. Recent investigations have revealed that the same Chinese hackers responsible for breaching the U.S. Treasury Department are now focusing on IT supply chains, raising significant concerns for both public and private sectors.

    The U.S. Treasury Breach: A Recap In a sophisticated cyberattack, hackers believed to be affiliated with the Chinese government infiltrated the U.S. Treasury Department, compromising sensitive data and potentially jeopardizing national security. The attack was part of a larger campaign targeting government agencies and private enterprises through vulnerabilities in widely used software solutions.

    Shifting Focus to IT Supply Chains Cybersecurity analysts and intelligence agencies have now identified that these hackers have expanded their focus to IT supply chains. By infiltrating software vendors and managed service providers, attackers can gain indirect access to numerous organizations that rely on these services, amplifying the potential damage.

    Tactics and Techniques Used The hackers employ advanced persistent threats (APTs) characterized by stealth, persistence, and high-level sophistication. Their tactics include:

    • Exploiting Zero-Day Vulnerabilities: Identifying and leveraging unpatched software flaws before they are widely known.
    • Supply Chain Infiltration: Injecting malicious code into legitimate software updates to gain entry into systems.
    • Credential Theft and Lateral Movement: Stealing credentials to move laterally within networks and escalate privileges.
    • Data Exfiltration and Espionage: Extracting sensitive information for political, economic, or military advantage.

    The Growing Risks to Organizations IT supply chain attacks pose a severe risk to organizations across industries, including finance, healthcare, and critical infrastructure. A successful breach can lead to data theft, financial loss, operational disruptions, and reputational damage. Governments and businesses must prioritize securing their supply chains through:

    • Enhanced Vendor Security Assessments: Conducting rigorous cybersecurity evaluations of third-party providers.
    • Zero-Trust Security Models: Implementing strict access controls and continuous authentication mechanisms.
    • Continuous Monitoring and Threat Intelligence: Proactively identifying and mitigating potential threats.
    • Incident Response Preparedness: Establishing robust response plans to quickly contain and remediate breaches.

    The resurgence of Chinese state-backed hackers targeting IT supply chains underscores the evolving nature of cyber threats. Organizations must remain vigilant, adopt advanced cybersecurity frameworks like the NIST Cybersecurity Framework (CSF), and foster collaboration between the public and private sectors to strengthen global cyber resilience. The battle against cyber espionage is ongoing, and proactive defense measures are the key to mitigating future attacks.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information.
  • Bybit Cryptocurrency Heist Traced to North Korean Cybercriminals

    Bybit Cryptocurrency Heist Traced to North Korean Cybercriminals

    In a shocking cyberattack, Dubai-based cryptocurrency exchange Bybit has suffered a massive security breach, losing approximately $1.5 billion worth of Ethereum (ETH) from one of its cold wallets. Multiple cybersecurity firms and blockchain analysts have found compelling evidence linking the heist to North Korea’s infamous Lazarus Group, a state-sponsored hacking collective known for large-scale financial crimes.

    A Sophisticated Attack

    The breach, which took place on February 21, 2025, involved a highly sophisticated manipulation of Bybit’s transaction system. Initial reports suggest that hackers exploited vulnerabilities in the transfer process between Bybit’s cold and hot wallets, effectively redirecting funds to an unauthorized address. Blockchain analysis firms Arkham Intelligence and Chainalysis have tracked the stolen funds to wallets historically associated with Lazarus Group operations.

    Cybersecurity researcher ZachXBT also corroborated these findings, identifying patterns similar to previous attacks executed by North Korean hackers. The group has a long history of targeting financial institutions and cryptocurrency exchanges to circumvent international sanctions imposed on North Korea.

    Bybit’s Response

    Despite the staggering loss, Bybit’s CEO, Ben Zhou, has assured users that the exchange remains financially stable. He emphasized that all client assets are backed 1:1 and that operations will continue without interruption. Bybit has launched a bounty program, offering up to 10% of the recovered funds to ethical hackers who can help track down and reclaim the stolen assets.

    The company has also engaged with global cybersecurity firms and law enforcement agencies to investigate the breach and strengthen its security infrastructure to prevent future incidents.

    A Growing Trend of Crypto Heists

    The Bybit attack marks the largest cryptocurrency theft in history, surpassing the $625 million stolen from Axie Infinity’s Ronin Network in 2022, which was also attributed to the Lazarus Group. Experts warn that North Korean hackers have been increasingly targeting digital assets as part of a broader strategy to fund the regime’s nuclear and missile programs.

    According to the United Nations, North Korea has stolen over $3 billion in cryptocurrencies since 2017, using sophisticated cyber tactics such as phishing campaigns, social engineering, and blockchain exploits. These attacks have prompted regulators and cybersecurity firms to call for stricter security measures and better cooperation among exchanges to combat the rising threat.

    The Road Ahead

    Bybit is working closely with blockchain forensic experts and financial regulators to track the movement of the stolen funds. However, the decentralized nature of cryptocurrency transactions makes it challenging to recover lost assets. Authorities are urging exchanges to implement advanced security protocols, including multi-signature authentication, AI-driven fraud detection, and real-time monitoring of transactions.

    As the cryptocurrency industry grapples with this latest breach, the Bybit heist serves as a stark reminder of the growing risks associated with digital asset storage and transfers. Experts continue to warn that unless proactive security measures are enforced across the industry, high-profile cyberattacks will remain a persistent threat.

    For now, the focus remains on tracking the stolen funds and holding those responsible accountable. Whether Bybit can recover its lost assets or if this attack will serve as another costly lesson in crypto security remains to be seen.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information.
  • Critical OpenSSH Vulnerabilities Expose Systems to Man-in-the-Middle and DoS Attacks — Patch Immediately!

    Critical OpenSSH Vulnerabilities Expose Systems to Man-in-the-Middle and DoS Attacks — Patch Immediately!

    Critical OpenSSH Vulnerabilities Discovered

    Security researchers have recently disclosed multiple vulnerabilities in OpenSSH, the widely used open-source implementation of the SSH protocol. These flaws could allow attackers to launch Man-in-the-Middle (MitM) attacks and Denial-of-Service (DoS) attacks, putting countless systems at risk. Organizations relying on OpenSSH for secure remote access should immediately patch their systems to mitigate these threats.

    Overview of the Vulnerabilities

    The newly identified vulnerabilities affect OpenSSH versions prior to the latest security patch. The two most critical flaws include:

    1. Man-in-the-Middle Attack Vulnerability(CVE-2024-####)
      • Attackers can intercept SSH traffic, potentially decrypting session data or injecting malicious commands.
      • This flaw stems from improper validation of SSH handshake integrity, allowing adversaries to manipulate authentication processes.
    2. Denial-of-Service (DoS) Vulnerability(CVE-2024-####)
      • Malicious actors can send specially crafted SSH messages, causing excessive CPU and memory consumption.
      • This can lead to system crashes or service disruptions, affecting business operations.

    Potential Impact on Organizations

    If exploited, these vulnerabilities could have severe consequences:

    • Compromised Authentication: Attackers can intercept or alter authentication requests, leading to unauthorized access.
    • Data Theft & Manipulation: Sensitive data transmitted over SSH sessions could be exposed.
    • Service Disruptions: Critical services relying on SSH for secure communications could be rendered inoperable.

    Mitigation & Recommended Actions

    Summit Systems ISSP strongly advises organizations to take the following actions immediately:

    1. Patch OpenSSH Immediately
      • Upgrade to the latest OpenSSH version that addresses these vulnerabilities.
      • Check official OpenSSH repositories and security advisories for the latest patch details.
    2. Enable Strict SSH Configurations
      • Use strict key exchange algorithms and disable outdated cryptographic protocols.
      • Implement multi-factor authentication (MFA) to enhance access security.
    3. Monitor & Audit SSH Traffic
      • Regularly review SSH logs for unusual login attempts or anomalies.
      • Deploy intrusion detection systems (IDS) to identify suspicious SSH activity.
    4. Restrict SSH Access
      • Limit SSH access to only necessary users and IP ranges.
      • Implement firewall rules to prevent unauthorized SSH connections.

    Conclusion

    With the growing threat landscape, ensuring the security of OpenSSH implementations is critical. Organizations should act immediately by applying patches, strengthening security configurations, and monitoring SSH activity. Summit Systems ISSP remains committed to helping businesses stay ahead of cyber threats through proactive security strategies.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information.
  • Microsoft Addresses Critical Authentication Bypass Vulnerability (CVE-2025-21396)

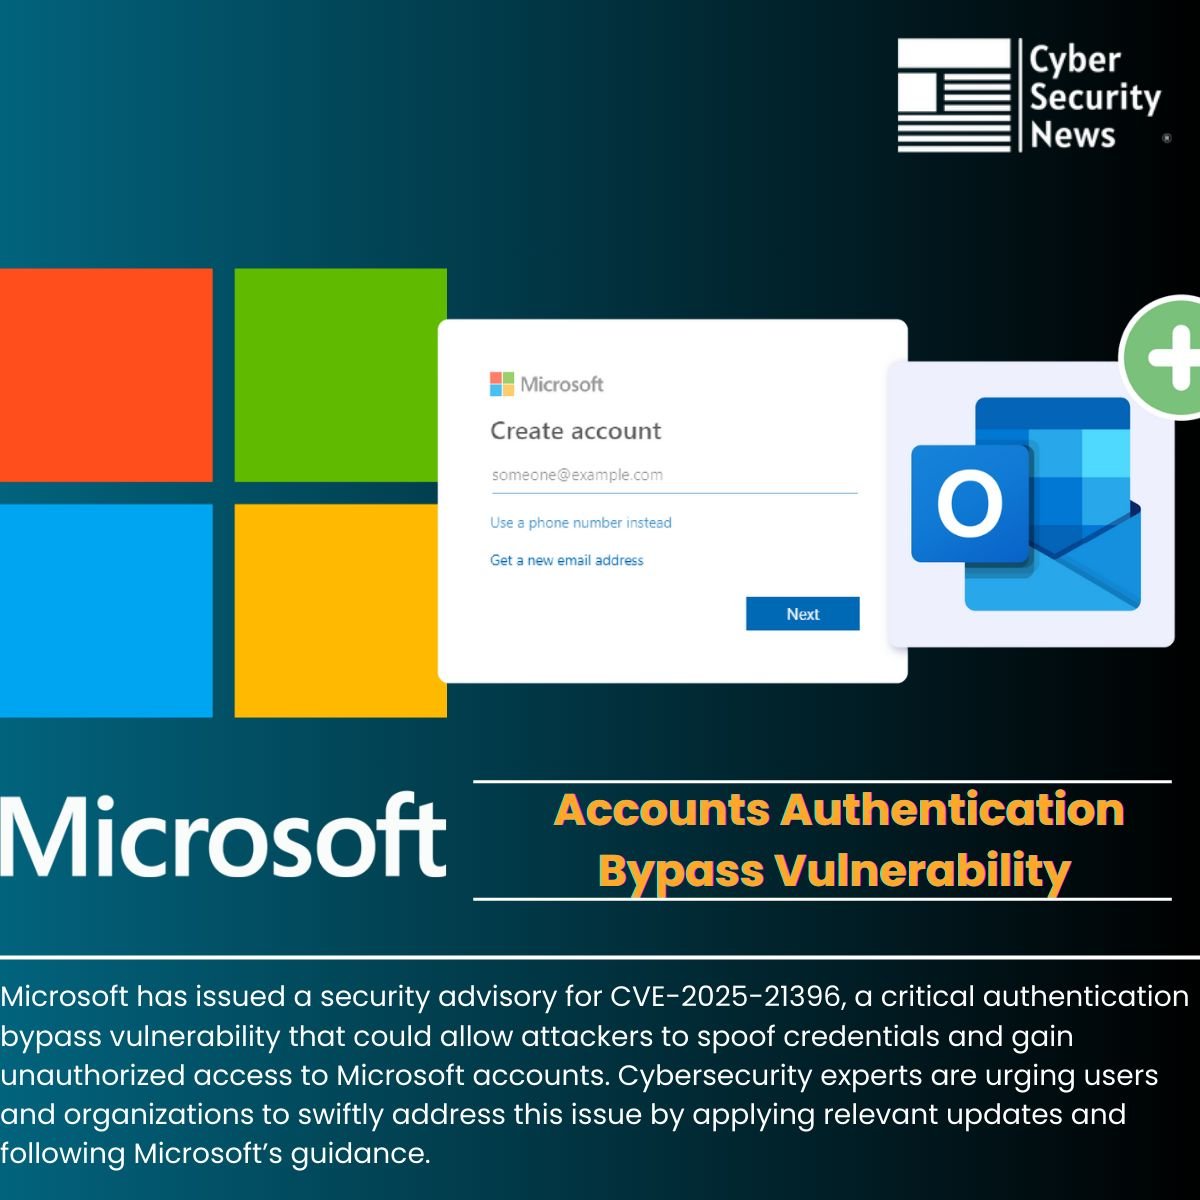
    Microsoft Addresses Critical Authentication Bypass Vulnerability (CVE-2025-21396)

    In a crucial security update, Microsoft has issued an advisory for CVE-2025-21396, a critical authentication bypass vulnerability that could enable attackers to spoof credentials and gain unauthorized access to Microsoft accounts. Summit Systems strongly advises organizations and individuals to take immediate steps to mitigate the associated risks.

    Understanding CVE-2025-21396

    CVE-2025-21396 is associated with CWE-290 (Authentication Bypass by Spoofing), a recognized security weakness affecting authentication mechanisms that lack robust validation methods. Malicious actors can exploit trust-based authentication models using techniques such as:

    • IP Spoofing: Attackers forge source IP addresses to impersonate trusted systems and gain unauthorized access.
    • DNS Spoofing: Manipulating DNS responses to redirect users to attacker-controlled domains.
    • Malformed or Manipulated Requests: Exploiting weak validation logic in application-layer protocols to bypass authentication measures.

    Due to the prevalent reliance on IP and DNS-based trust models, this vulnerability poses a significant risk, necessitating immediate remediation.

    Attack Scenarios and Potential Impact

    The vulnerability may be exploited in multiple ways, including:

    • Bypassing IP-Based Authentication: Organizations that rely solely on IP addresses for authentication may be at risk, as attackers can forge IP addresses to appear as trusted entities, bypassing security measures.
    • DNS-Based Host Verification Manipulation: Attackers can poison DNS caches, causing systems to trust a malicious domain masquerading as a legitimate Microsoft service.

    Considering the relative ease of executing IP spoofing and DNS cache poisoning attacks, CVE-2025-21396 is classified as a critical vulnerability with a high likelihood of exploitation.

    Microsoft’s Security Guidance & Recommended Mitigations

    Microsoft has issued patches to address CVE-2025-21396 and urges all users and organizations to apply security updates without delay. Summit Systems further recommends the following best practices:

    1. Apply Security Updates: Regularly update all systems and software by following Microsoft’s Security Update Guide.
    2. Strengthen Authentication Mechanisms:
      • Implement Multifactor Authentication (MFA) for enhanced security.
      • Utilize cryptographic tokens for secure identity validation.
      • Deploy Mutual TLS (mTLS) for encrypted and authenticated connections.
    3. Monitor Networks for Anomalies: Deploy Intrusion Detection Systems (IDS) to detect spoofed packets and unusual DNS activity.
    4. Harden DNS Infrastructure: Implement DNS Security Extensions (DNSSEC) to safeguard against DNS spoofing and maintain data integrity.
    5. Enable Logging & Auditing: Maintain comprehensive logs of authentication attempts to facilitate forensic analysis in the event of an attack.

    While Microsoft has addressed CVE-2025-21396 with the latest security updates, organizations must take proactive measures such as strengthening authentication frameworks and enhancing network monitoring to reduce exposure to similar threats in the future.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information.
  • Massive PowerSchool Data Breach Exposes Millions of Student and Educator Records

    Massive PowerSchool Data Breach Exposes Millions of Student and Educator Records

    The education sector is facing one of the most significant data breaches in recent history, as PowerSchool, a leading provider of Student Information Systems (SIS) in the U.S. and Canada, confirmed that hackers had stolen vast amounts of historical data from school districts. The breach, which has already impacted millions of students and educators, raises serious concerns about data security in educational institutions.

    On January 7, 2025, PowerSchool disclosed that attackers had accessed its SIS service through the PowerSource customer support portal. This breach enabled them to steal extensive personal data, including:

    • Names and contact information
    • Dates of birth
    • Medical records
    • Social Security numbers
    • Disability information
    • Race, ethnicity, and gender data
    • Parent/guardian/emergency contact details

    School districts confirmed that records dating back to 1985 were compromised, impacting over 72 million individuals, including 62.5 million students and 9.5 million educators across the U.S. and Canada.

    How Did This Happen?

    PowerSchool initially cited a “compromised credential” as the entry point for the breach. The Menlo Park City School District (MPCSD) reported that the compromised credential belonged to a maintenance account, granting broad access to customer data. Security researchers suspect that information-stealing malware may have been used to obtain this login information.

    The breach was detected on December 28, 2024, but evidence suggests that hackers had been exfiltrating data since December 22 using an export data manager. Despite working with cybersecurity firm CrowdStrike to investigate the breach, PowerSchool has not publicly disclosed further details about the attack.

    A Growing Crisis: Lawsuits and Fallout

    As more school districts reveal the extent of their data exposure, legal and reputational consequences for PowerSchool continue to mount:

    • Over 20 lawsuits have already been filed against the company.
    • School districts, including the Toronto District School Board (TDSB), reported that 1.5 million students were affected.
    • Data from 6,500 school districts may have been stolen, making this one of the largest education sector breaches to date.

    Despite claims that the stolen data was deleted after a ransom payment was made, PowerSchool is providing impacted individuals with two years of free identity theft and credit monitoring services.

    What Can Schools and Educators Do?

    Given the scale of this breach, affected institutions and individuals must take proactive steps to protect their data:

    1. Review Security Logs – Schools using PowerSchool’s SIS should analyze logs to determine the extent of data exfiltration.
    2. Monitor for Identity Theft – Impacted individuals should take advantage of PowerSchool’s credit monitoring offer and watch for suspicious activity.
    3. Strengthen Authentication Measures – Institutions should implement multi-factor authentication (MFA) and regularly rotate administrative credentials.
    4. Enhance Cybersecurity Training – Educators and administrators should be trained on recognizing phishing attempts and safeguarding sensitive information.

    Final Thoughts

    This breach highlights the urgent need for stronger cybersecurity measures in the education sector. Schools must reassess their security strategies to prevent future incidents, and vendors like PowerSchool must ensure that their systems are more resilient against cyber threats. Summit Systems is committed to helping organization bolster their cybersecurity defenses through advanced risk management strategies and compliance solutions.

    Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Summitsystemsissp assumes no liability for the accuracy or consequences of using this information.